What if the next national-security threat isn’t coming through your front door, but through your driveway? Your car can collect sensitive data, communicate with outside networks, and rely on software that most drivers know nothing about. Now Congress is sounding the alarm over connected-vehicle technology tied to China and other foreign adversaries. If a hostile government could exploit those connections, the stakes go far beyond your privacy. We’re talking about potential access to Americans’ movements, sensitive information, and vehicle systems. Who controls that technology, and how do we know it can be trusted?
This is no longer just a debate about where a car is built. It is about who controls the technology inside it, what information that technology can access, and whether Americans understand the risks that come with driving a connected vehicle.
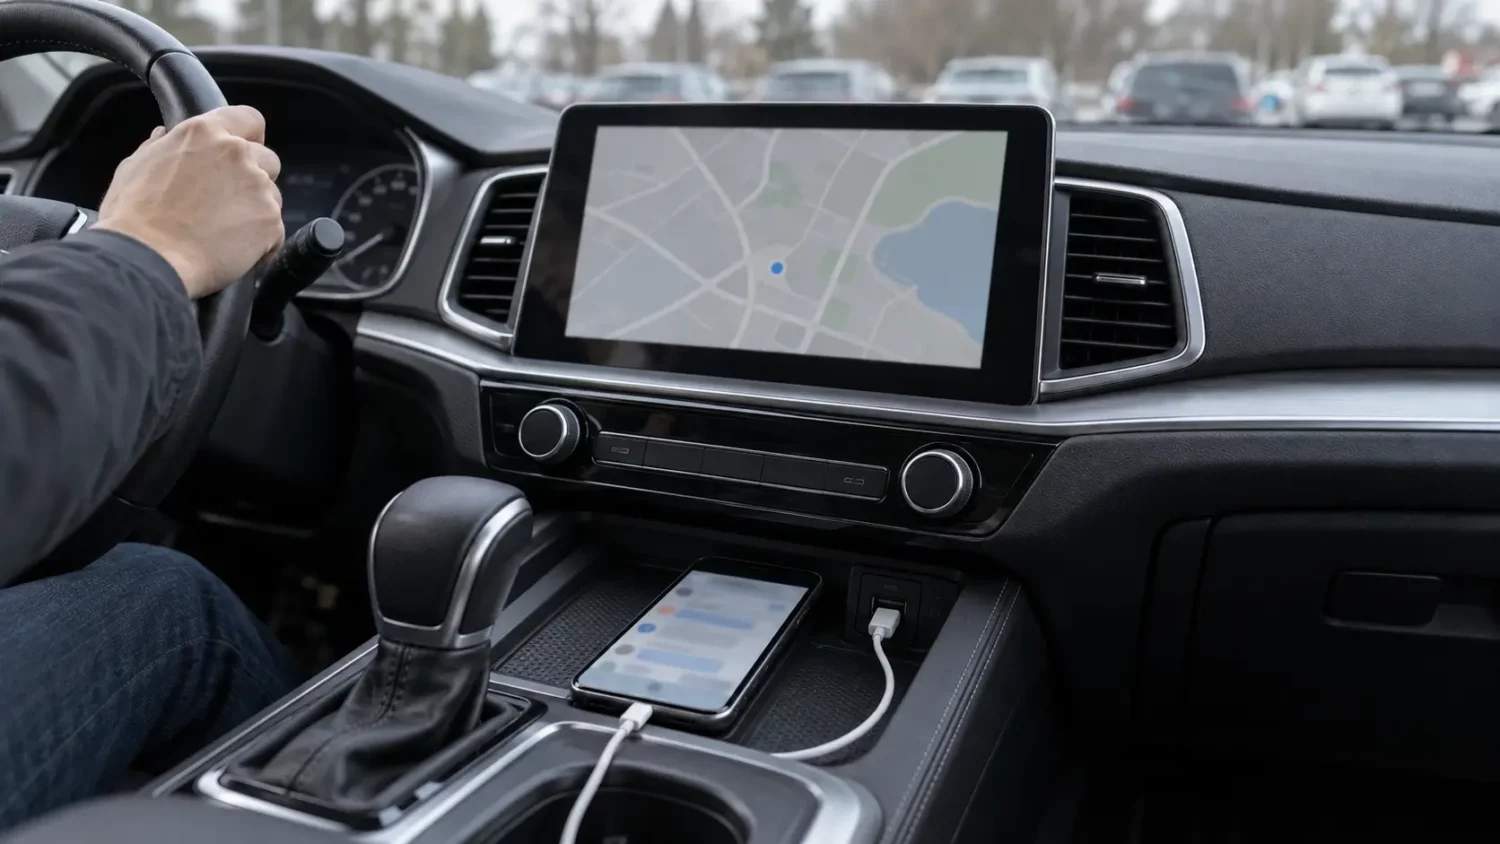
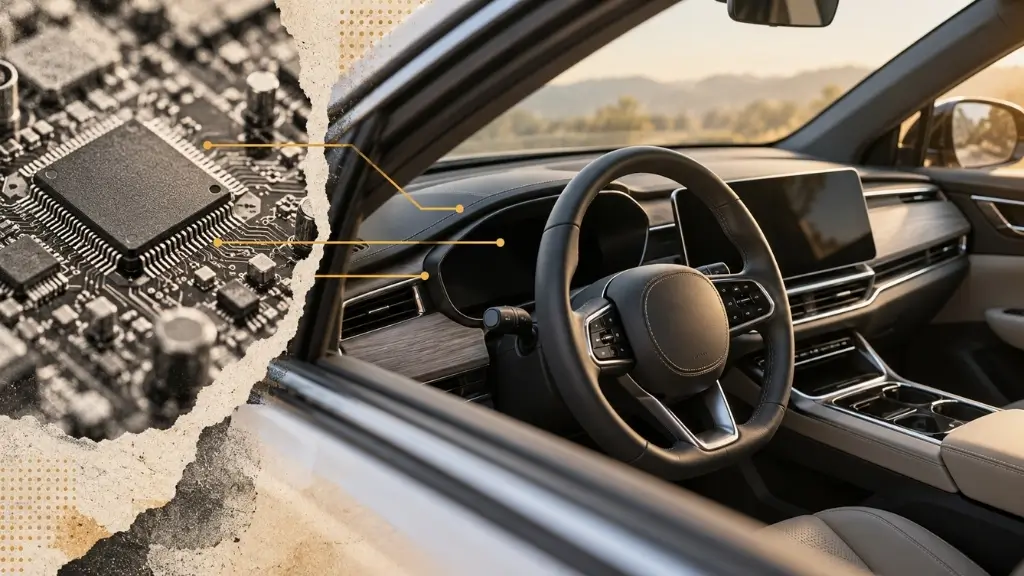
Modern cars are rolling computers. They rely on wireless communications, navigation, software updates, telematics, cameras, and sensors that can gather and transmit information. Those connections can make driving safer and more convenient, but they also create potential points of vulnerability. The auto industry has raced to add more technology to vehicles, while consumers have largely been left to trust that someone, somewhere, is making sure it is secure.
That trust deserves scrutiny.
Your Car Is More Connected Than You Think
The concern is not imaginary. In February 2024, the U.S. Department of Commerce launched an investigation into national security risks involving connected vehicles and technology linked to China. Officials raised concerns about sensitive data collection and the possibility that compromised technology could be used to manipulate or disable vehicles. The administration later finalized a rule restricting certain connected-vehicle software and hardware transactions associated with China and Russia.
Let’s be clear: identifying a vulnerability is not proof that a manufacturer is spying on American drivers. But waiting for a security failure before asking who has access to vehicle data would be an astonishingly reckless way to protect the public. The question is whether the United States is identifying and addressing these risks before connected technology becomes even more deeply embedded in everyday life.
Congress Is Looking Beyond the Badge on the Hood
The congressional debate reflects a growing recognition that connected-vehicle security cannot be reduced to a marketing label or a country-of-assembly sticker. Software, electronic control systems, communications equipment, and supply chains can cross international borders, even when a vehicle is sold by a familiar American or European brand.
The proposed Connected Vehicle Security Act of 2026 seeks to address risks associated with connected vehicles and related technology tied to foreign adversaries. It is part of a broader fight over how the United States should control technology that could expose sensitive data or create national security vulnerabilities.
But introducing a bill is not the same as passing a law. Congress still has to determine the scope of any restrictions, how they will be enforced, and how legitimate security concerns will be balanced against competition, innovation, and consumer choice.
That is where the details matter. Broad promises about protecting Americans mean very little without clear standards, meaningful oversight, and accountability for companies that fail to meet them.
Who Protects the Driver?
National security is only one piece of this puzzle. Consumers also deserve straightforward answers about what their vehicles collect, where that information goes, how long it is retained, and who can access it.
Those questions apply across the automotive industry, not just to technology connected to China. A connected vehicle can raise privacy concerns regardless of the country associated with its software or hardware. Drivers should not have to become cybersecurity experts just to understand what happens to their personal information when they get behind the wheel.
Automakers have spent years selling connectivity as a benefit. Now they need to explain the responsibilities that come with it. If vehicle technology can collect sensitive information or communicate with remote systems, manufacturers should be able to explain how those systems are secured, what data is necessary, and what protections prevent unauthorized access.
Consumers should not have to choose between modern features and reasonable expectations of privacy.
Washington Must Finish What It Started
The United States cannot afford to ignore genuine national security risks simply because addressing them is complicated or commercially inconvenient. At the same time, officials must distinguish documented threats from speculation, write rules that can be enforced, and explain exactly what is being restricted and why.
Congress has an opportunity to get this right, but passing legislation is only the beginning. Oversight, transparent standards, and consequences for noncompliance will determine whether these efforts actually protect Americans.
The automotive industry is entering an era in which software and data may matter as much as engines and transmissions. That makes one question unavoidable: When your car collects information about your life, who ultimately controls it, you, the company that built the vehicle, or someone you never agreed to trust?
Americans shouldn’t have to wonder whether the technology in their driveway could threaten their privacy or national security, and Congress must deliver answers before the risks become reality.
Check out my full commentary on this story: https://youtu.be/exiOeOJy0ss
Looking for more automotive news? https://www.CarCoachReports.com
Listen and subscribe to The Drive with Lauren and Karl – https://www.youtube.com/@thedrivecarshow